The Thunderfury Incident
"Did someone say Thunderfury, Blessed Blade of the Windseeker?" — The IT Department, probably
I have a confession: early in college, I casually played World of Warcraft (WoW). With that off my chest, let me tell you about the time I almost got into trouble over a shell script. And how WoW was involved.
To set the scene: I was in campus housing, just getting started in Linux land, trying to master the shell. I mostly tinkered on my MacBook, but we had access to shared, virtual Linux workstations. Think of it as a free timeshare for college students. I realized something: I could broadcast messages to everyone else logged into the same machine via wall. I also had access to about 40 shared workstations across the network.
So I wrote a script and tested it for a couple of minutes in a computer lab. I got my confirmation from the confused looks on people's faces. Each person on a workstation would be spammed randomly with the simple message: “Did someone say Thunderfury, Blessed Blade of the Windseeker?”.
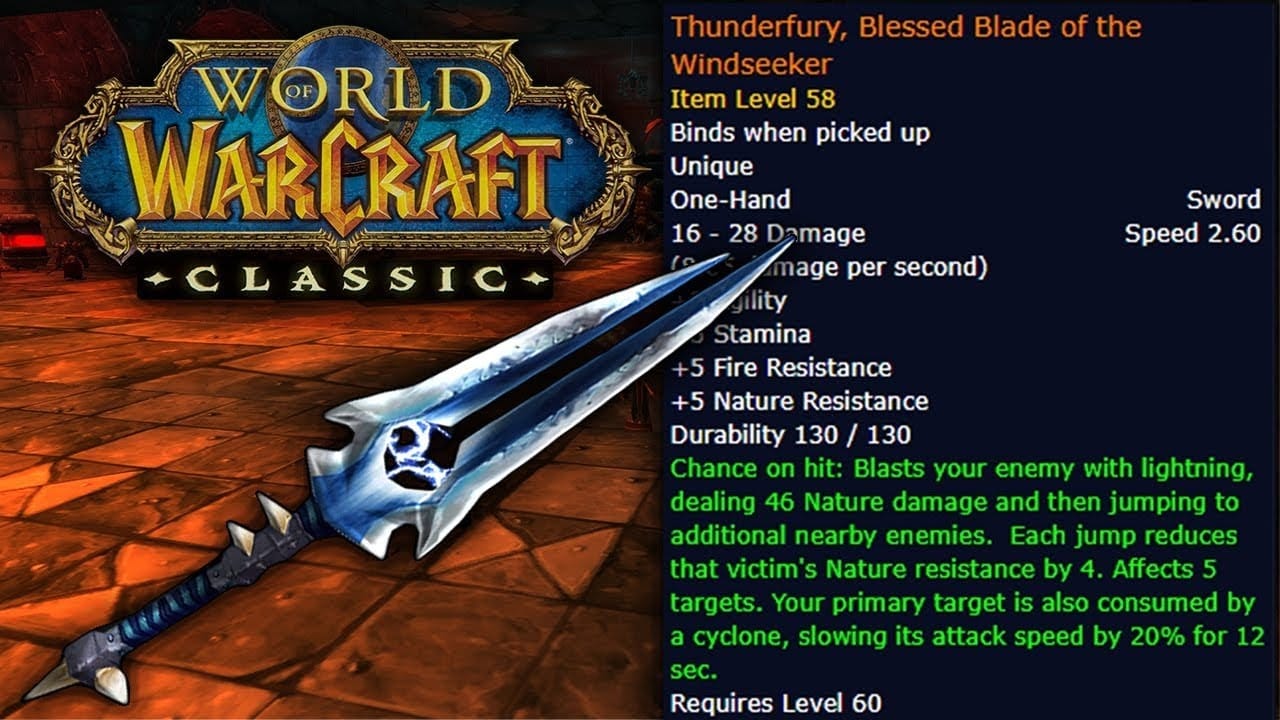
A day or so later, I was hanging out in the computer science lounge, talking to a friend who happened to grade for the introductory programming class. He was eager to tell me my script had hit a student’s assignment submission and muddled it. The student went to the teacher and accused me of hacking their computer. Amused, the teacher just said “oh, that’s just Illya” and graded over it.
But, how did they know it was me?
See, my script had a bit of a flaw. The -n flag in wall suppresses the banner that shows who sent the message; omitting it broadcasts your message with your username attached. So there was no hiding from it, which is why I only gave it a “light test run.”
I gave it a couple of weeks and didn’t hear anything about it. So I published a blog post, shell script attached, and called it a day. Coast was clear.
Until a few months later, when I got a text from a friend that worked in the IT department. They were upset about my shell script. And they weren’t upset that I ran it, they were upset I published it on my blog.
Now, I was worried. They were meeting later in the day to decide what action to take. I held my breath and took down the page. I got a follow-up that everything would be okay. I asked my friend to apologize on my behalf, and I wouldn’t do it again. And that’s the last I heard of it.
So, here’s that blog post.
If your school is anything like mine (engineering and science, mostly), you probably have some kind of virtual Linux machines you can SSH into. If you’ve done any digging, you might have realized that commands such as wall or write are not disabled. If you are anything like me, you probably thought about writing a shell script that will automatically log you in, spam something (i.e. the famous Thunderfury, Blessed Blade of the Windseeker) on a random machine, and leave. Well you’re in luck.
#!/bin/bash

PASSWORD="your-password-here"
USERNAME="your-username"
HOST_PREFIX="linux"
MIN_HOST=1
MAX_HOST=39
MESSAGE="Did someone say [Thunderfury, Blessed Blade of the Windseeker]?"

spam() {
    local n=$(( RANDOM % (MAX_HOST - MIN_HOST + 1) + MIN_HOST ))
    local host
    printf -v host "%s%02d" "$HOST_PREFIX" "$n"

    sshpass -p "$PASSWORD" ssh -t -l "$USERNAME" "$host" \
        "printf '%s\n' '$MESSAGE' | wall"
}

while :; do
    spam
    sleep $(( RANDOM % 60 + 1 ))
done
Set PASSWORD, USERNAME, and HOST_PREFIX up top. MIN_HOST and MAX_HOST bound the random suffix, zero-padded to two digits (so linux01 through linux39). The loop fires on a random 1-60 second interval. Neat!